


The OLOID Blog
Insights on identity, access, and security for the modern frontline workforce.
Featured
Imprivata Competitors and Alternatives: 10 Clinical Access Platforms Compared
Imprivata competes across several product lines, so the right alternative depends on which module you want to replace. This guide maps Imprivata’s products to competitor categories and sets seven clinical evaluation criteria. It compares 10 Imprivata alternatives on the same terms, from OLOID and AuthX to Duo, Entra ID, and Okta. It covers why hospitals review Imprivata at renewal, including cost, vendor sprawl, and ownership changes. It also explains when staying with Imprivata makes sense.

How MFA Works in POS Systems
MFA for POS systems verifies employees, separate from cardholder payment authentication. It applies at register login, manager overrides, back office, vendor access, and admin portals. PCI DSS 4.0.1 requires MFA for all CDE access and sets replay, bypass, and independence rules. The cashier exemption is narrow and leaves overrides and admin access in scope. Badge and face factors keep shared registers fast and every session attributable.
Passkey Security Risks and How to Reduce Them
Passkeys resist phishing, but attackers now target the processes around them. 2026 research from SpecterOps and Unit 42 exposed replay and sync extraction paths. The seven core risks span enrollment, recovery, sync, endpoints, validation, sessions, and prompts. Shared devices and frontline workflows multiply these risks. A hardening checklist closes most gaps without slowing the rollout.
9 Considerations for Multifactor Authentication in Healthcare
Multifactor authentication in healthcare protects ePHI, but standard MFA assumes one user per device and a phone in every pocket. This guide explains what counts as MFA, where HIPAA and DEA rules stand, and how the proposed Security Rule changes the picture. It walks through nine considerations, from shared workstations and PPE to break-glass and vendor access. Two comparison tables match MFA methods to clinical workflows, followed by a phased rollout plan with metrics to track.
Session Timeout Best Practices
A session timeout ends an authenticated session after a set period of inactivity or a fixed total duration, which limits how long a stolen or abandoned session stays useful. Recent token replay attacks show that a hijacked session gives attackers the same access a password would, for as long as the session lives. This guide covers the four timeout types, recommended values by risk level based on NIST, PCI DSS, and HIPAA, server-side enforcement, and the settings that quietly defeat timeouts. It also explains why timers fail on shared workstations and how presence-based locking ties each session to one verified worker.
Pass-the-Hash Attacks: How They Work, Detection, and Prevention
A pass-the-hash attack lets an attacker reuse a stolen NTLM password hash to authenticate as a user without cracking the password. It remains a common lateral movement technique in ransomware intrusions because NTLM is still enabled across most Windows networks. This guide covers how the attack works, the Windows events that reveal it, and the controls that prevent it. It also explains why MFA alone does not stop hash replay and why shared frontline workstations carry higher risk.
Break Glass Access: How Emergency Access Works and How to Keep It Accountable
Break glass access is a pre-approved way to bypass normal access controls during an emergency, using credentials reserved for that purpose and audited on every use. It covers both IT emergency accounts used when SSO, PAM or MFA fails, and break-the-glass overrides that let clinicians open restricted EHR records. This guide explains when organizations need break glass access, what HIPAA requires, and how to set up a break glass procedure with phishing-resistant authentication. It also covers the risks that weaken emergency access, especially shared credentials on frontline workstations.
10 Common HIPAA Violations and How to Prevent Them
The most common HIPAA violations include employee snooping, shared logins, missing risk analysis, unencrypted devices, impermissible disclosures, denied patient access, missing BAAs, late breach notices, and improper disposal. This guide pairs each violation with a real OCR settlement and the control that prevents it. It covers 2026 penalty tiers, how OCR finds violations, and why shared logins on shared workstations turn individual mistakes into organizational findings.
Privilege Creep: Causes, Risks, Examples, and How to Prevent It
Privilege creep is the gradual accumulation of access rights beyond what a user, account, or system needs for its current role. It builds because organizations have a process for granting access and none for removing it, so every promotion, project, and covered shift becomes a permanent addition. This guide covers what causes it, how it creates toxic combinations that break segregation of duties, and why quarterly access reviews miss it. It also covers how shared workstations and non-human identities hide it, and the detection and prevention steps that stop it at the source.
Mandatory Access Control (MAC): How It Works, Examples, and Limitations
Mandatory access control is the authorization layer of IAM, granting access only when a user’s clearance matches a resource’s security label. This guide explains how MAC makes each access decision, the Bell-LaPadula and Biba models behind it, and real examples across healthcare, manufacturing, retail, and logistics. It compares MAC with DAC, RBAC, and ABAC, outlines a practical implementation path, and covers its benefits and limits. It also shows why shared logins and shared workstations break MAC, and how passwordless authentication ties every session to a verified person.
Accountability in IAM: The Missing Layer in Shared-Workforce Security
Accountability is the third pillar of IAM, alongside authentication and authorization, and the one most organizations assume rather than build. On shared devices and shift-based teams, the account and the person often diverge, so logs record an account that several workers used. That gap weakens behavioral detection, slows incident containment, and leaves shared credentials active long after workers leave. This piece explains where frontline attribution breaks down and what it takes to build accountability into every session.

Security Doesn't End When Access is Granted
Most identity programs focus on the login, but the real exposure often sits in the hours that follow. Stolen session tokens bypass MFA, shift-long sessions outlast the conditions that justified them, and shared devices change hands without any alert. This blog explains why timeouts and SSO leave gaps on busy frontline devices, how step-up verification protects high-risk actions, why disabled accounts can keep working through open sessions, and four questions leaders can use to measure security after login.

What is Fast User Switching: How It Works and Where It Breaks
Fast user switching lets a new user take over a shared device in seconds without a full logout, so every action stays tied to a verified individual. Most organizations treat it as a convenience feature and miss how much the implementation model matters. In a healthcare environment, where identity lives, how the previous session is handled and which authentication method healthcare professionals use decide whether switching protects the audit trail and the patient record or quietly breaks them. This guide covers the four switching models, their real-world failure points in clinical workflows, what an auditable switch records, and how to evaluate solutions for shared clinical workstations.
Passwordless Clinical Workflows: A Practical Guide
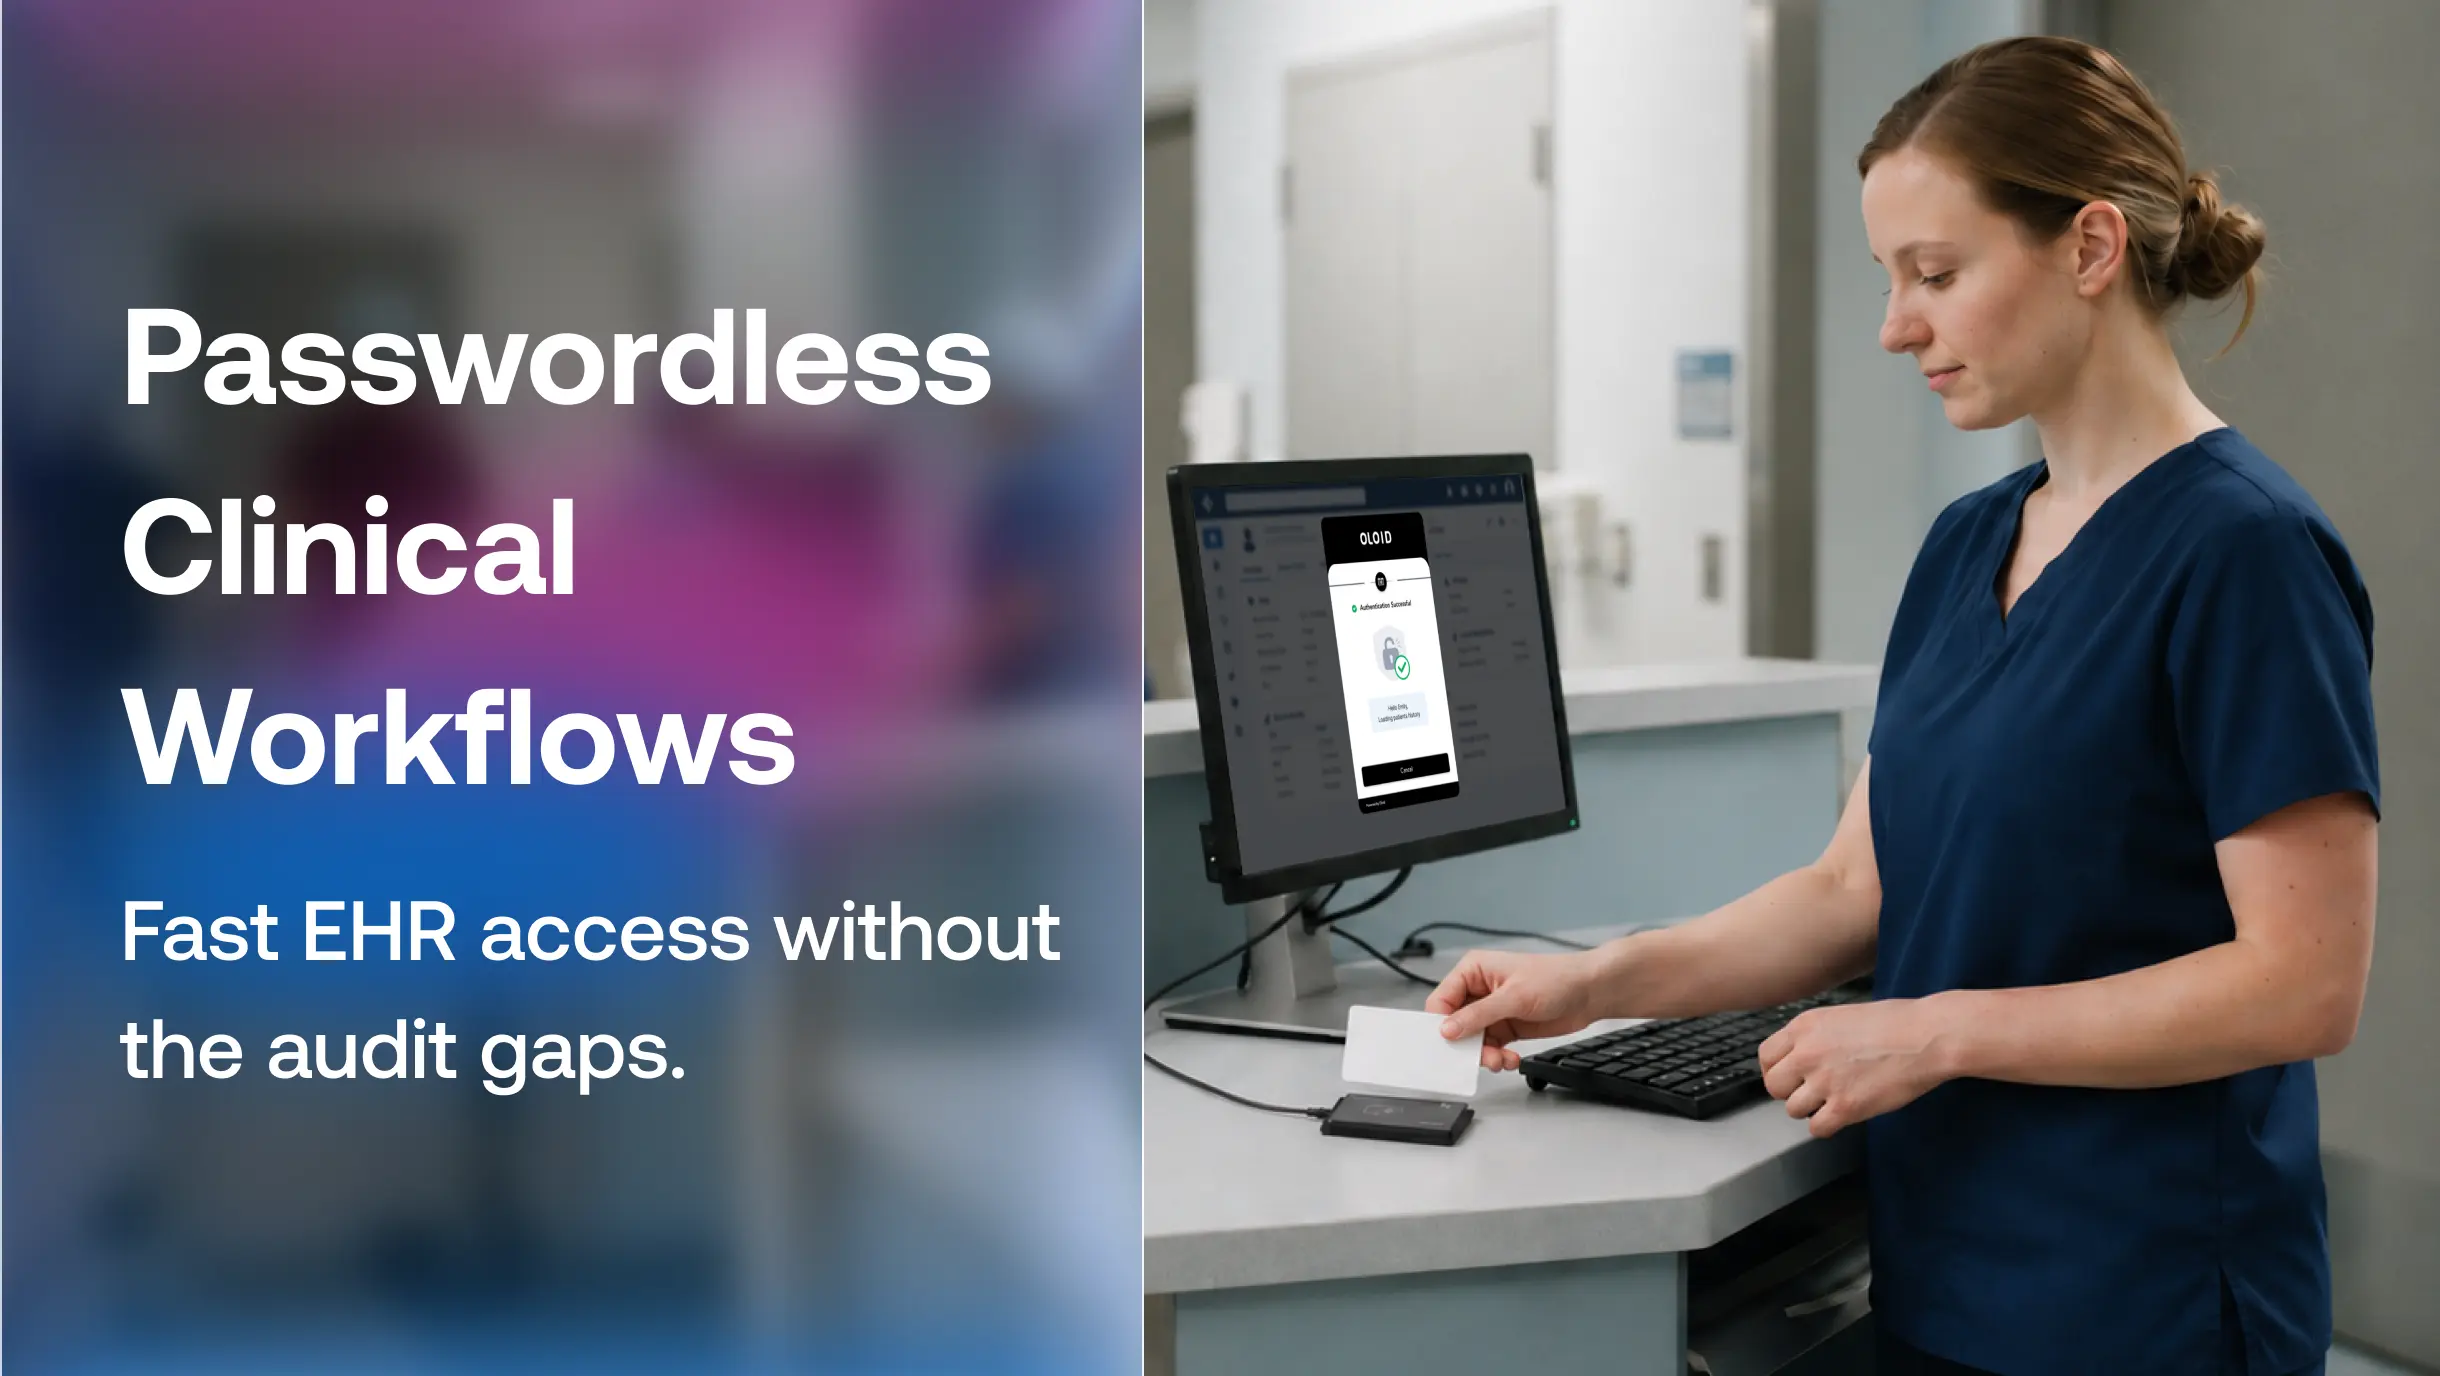
Passwordless authentication in healthcare replaces typed passwords with badges, biometrics, and passkeys that tie every clinical session to a verified individual. Shared workstations break the one-person-per-device model most identity tools assume, which drives open sessions, credential sharing, and broken audit trails. This guide compares passwordless methods for clinical settings and explains risk-based step-up for EPCS. It also covers identity across the clinician lifecycle, HIPAA and DEA alignment, and a phased rollout with measurable KPIs.
NIST Zero Trust Architecture: A Practical Guide
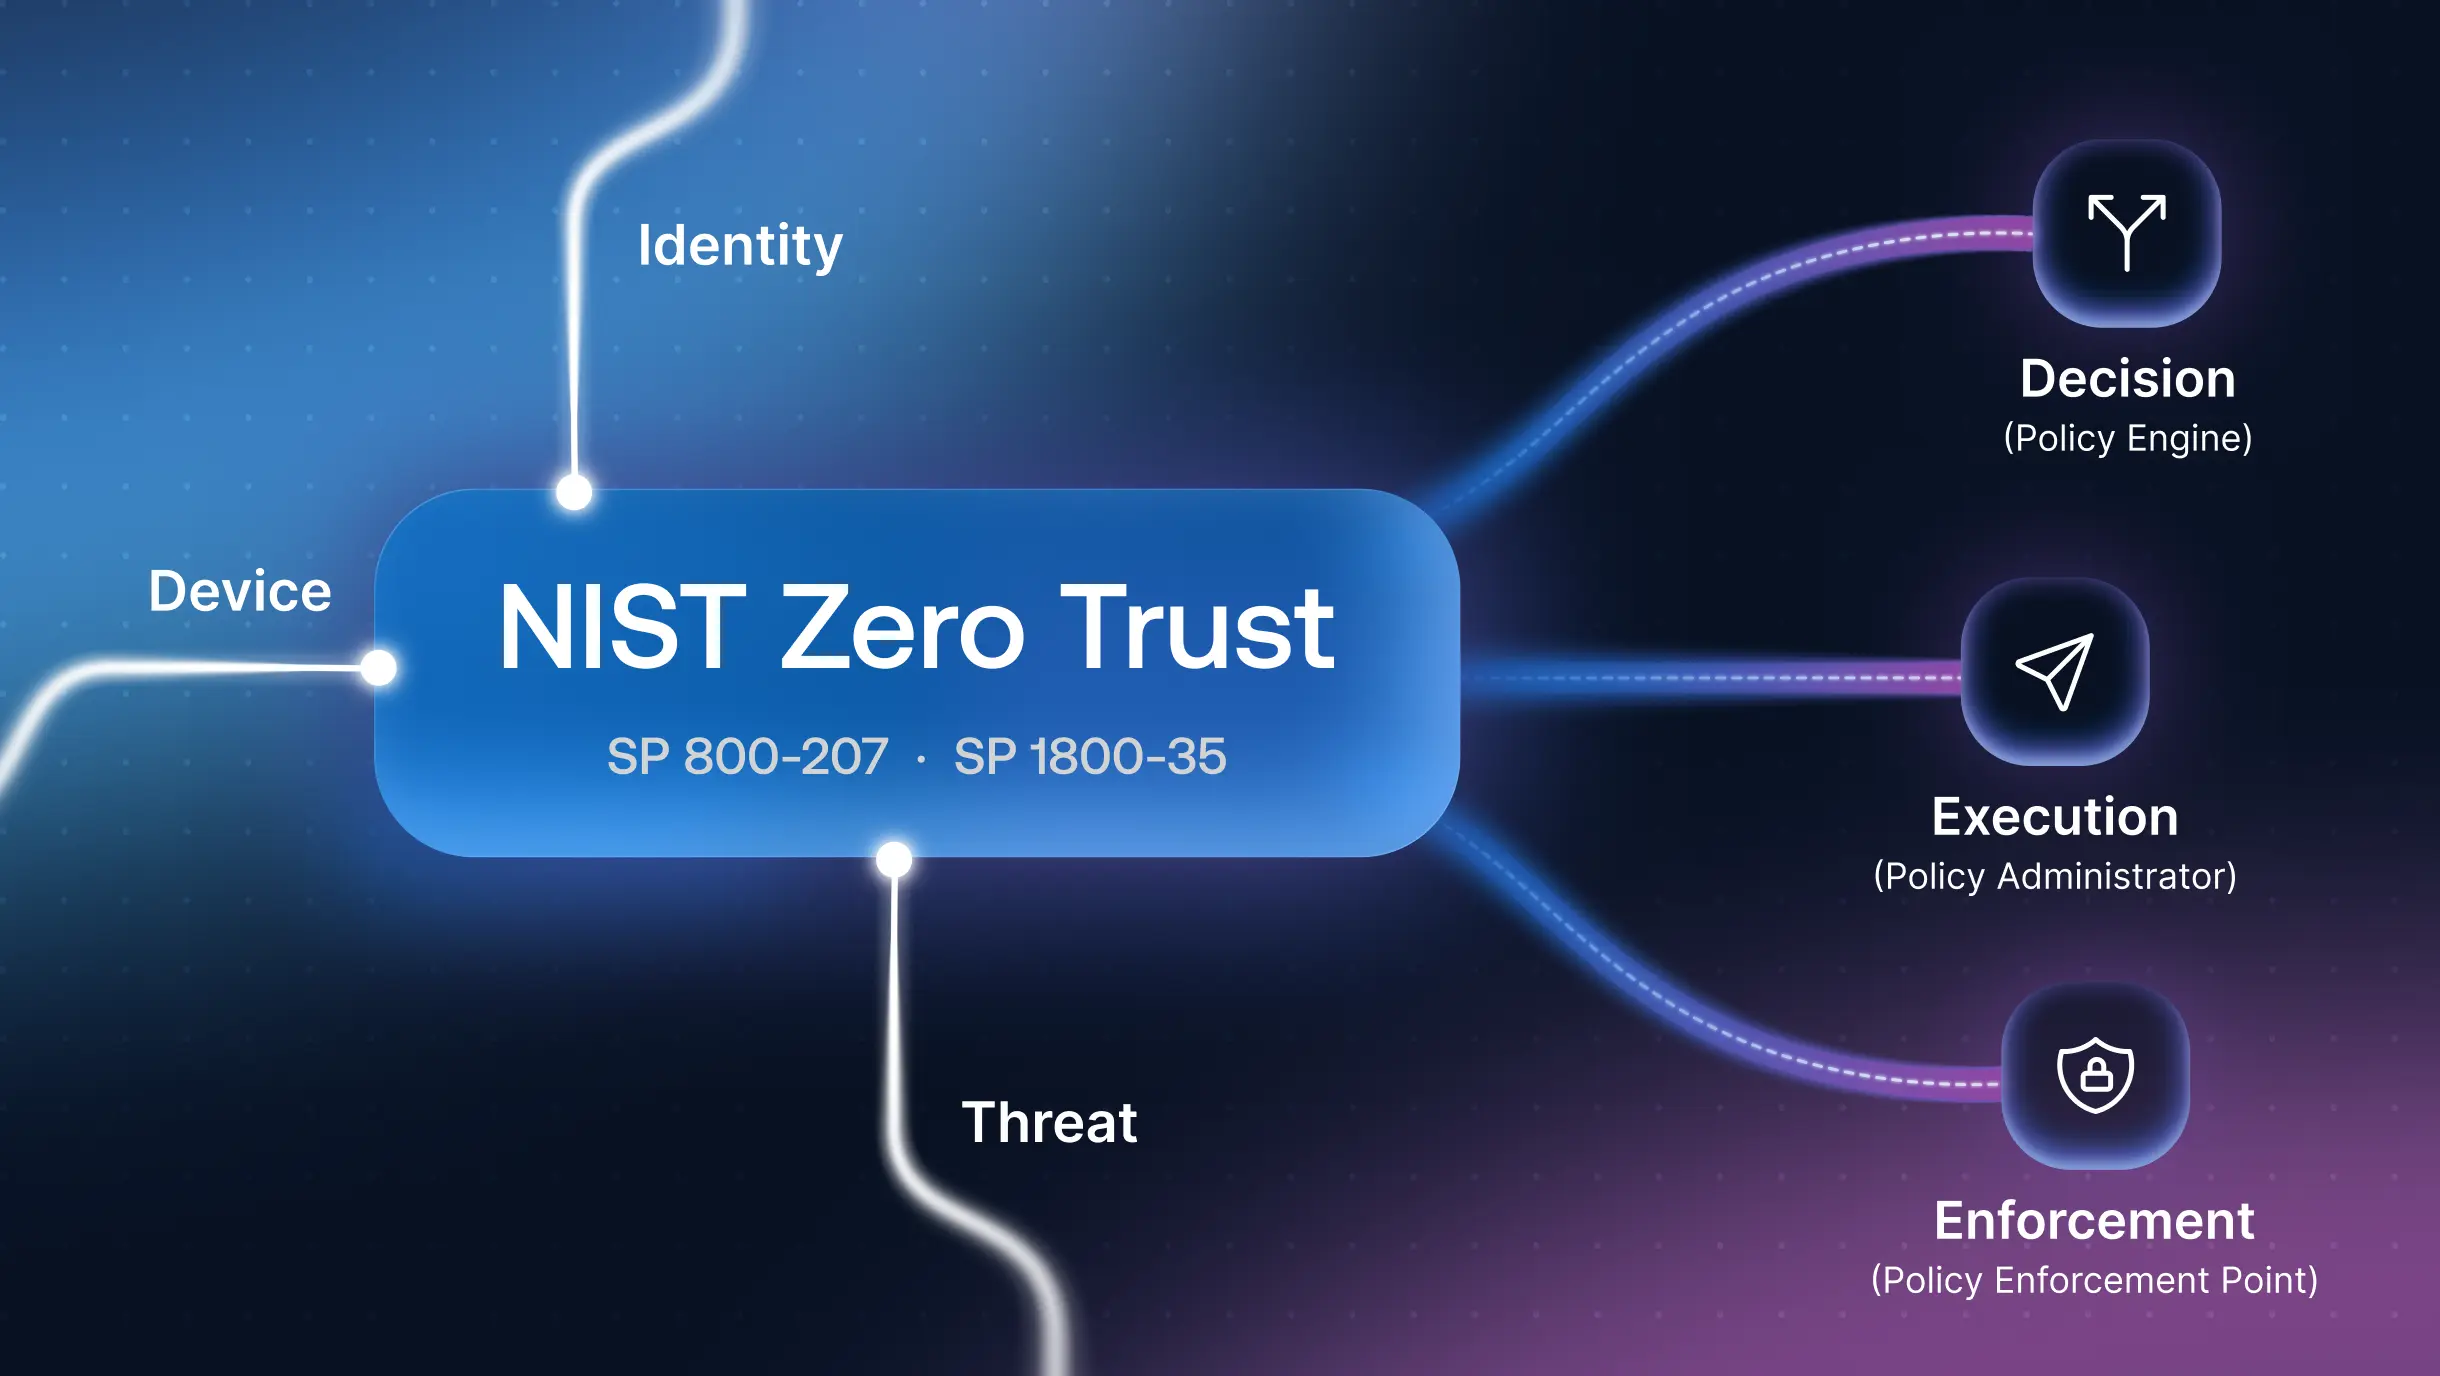
NIST zero trust architecture is a vendor-neutral security model that evaluates every access request using identity, device posture, and context instead of network location. SP 800-207 defines the model, and SP 1800-35 tests it through 19 implementations built with 24 vendors. This guide explains the reference components, how trust decisions are made, and what NIST's own builds revealed about integration gaps. It also covers the blind spot most programs miss: shared devices and frontline workers, where healthy endpoints can hide unverified users.
Passkey Enterprise Challenges: Why Frontline Environments Break the Model
Passkey enterprise challenges go deeper than legacy system integration and cross-platform fragmentation. The deployment gap most organizations do not plan for is workforce segmentation: standard passkey architecture, both device-bound and synced, was built for knowledge workers on managed devices, not for frontline workers rotating through shared terminals across shifts. This post covers where passkey deployment breaks structurally in shared-device environments, why compliance mandates accelerate pressure without solving the frontline problem, and what an authentication architecture that accounts for the full workforce actually looks like.
Multi-Factor Authentication Examples: Methods, Use Cases, and Best Practices
This guide covers the most common multi-factor authentication examples across the three-factor categories, comparing SMS OTPs, TOTP, push notifications, biometrics, and hardware security keys on security strength and operational fit. It maps MFA method selection to industry context including healthcare, manufacturing, financial services, and retail, and addresses where standard MFA breaks down on shared terminals when sessions are not tied to individual workers. The post closes with how passwordless authentication closes the individual attribution gap that conventional MFA leaves open in shift-based environments.
What is Privileged Identity Management (PIM)?
Privileged identity management (PIM) governs the lifecycle of elevated access roles: who holds them, under what approval, and for how long. This guide covers how PIM differs from PAM and IAM, how the role lifecycle works from request through automatic revocation, and why PIM breaks down in shared-device and frontline environments where multiple workers share terminals. It covers compliance requirements under HIPAA, PCI DSS, SOC 2, and NIST 800-53, and explains what individual-level attribution actually requires at the point of access. Practical best practices and a phased starting point are included.
What is Identity Lifecycle Management?
Identity lifecycle management (ILM) governs every digital identity in an organization from creation to deactivation, covering employees, contractors, vendors, and non-human identities. This guide covers the joiner-mover-leaver model, what breaks when ILM is poorly managed: orphaned accounts, privilege creep, stale access, and why the standard model struggles in high-turnover, shared-device environments. It covers compliance exposure under HIPAA, PCI DSS, and CMMC, and explains how passwordless authentication closes the individual attribution gap that shared terminals create.
10 Best Biometric Authentication Solutions in 2026
Most biometric authentication blogs cover desk workers and consumer onboarding. This guide evaluates 10 platforms against the criteria that matter for both populations, with particular depth on frontline and shared device environments where standard platform biometrics fail. OLOID leads as the only purpose-built solution for phone-restricted, shared terminal environments. Windows Hello for Business, Imprivata EAM, HYPR, Cisco Duo, Ping Identity, BlueFletch, 1Kosmos, AuthX, and HID Global each earn their place for specific environments.
6 Best Authentication Solutions for Shared Devices in 2026
Most authentication platforms assume one person per device. This guide evaluates six solutions against the criteria that matter for shared terminals: individual session attribution, phone-restricted environment support, shift-change speed, offline capability, and compliance-ready audit logs. OLOID leads as the only purpose-built platform for this use case. Microsoft Entra ID, Okta, HID Global, Ensurity, and Imprivata each earn their place for specific environments.
Compliance Verifies Policies, Not the People Behind the Login
Compliance frameworks like HIPAA, FDA 21 CFR Part 11, and SOX all rest on one assumption: every access event traces to a specific individual. Shared credentials in frontline environments quietly break that assumption while producing logs that look clean. This post unpacks the gap between access logged and person accountable, and what it takes to close it in shared-device environments.


Authentication Friction on the Frontline Becomes a Security Risk
Authentication friction on the frontline isn't just a usability complaint. It's the direct cause of shared credentials, persistent sessions, and broken audit trails that compliance frameworks can't account for. This post makes the case that frictionless, person-bound authentication is security work, not a nice-to-have, and explains what that looks like in environments where standard MFA was never designed to operate.
What is Credential Harvesting? How It Works and How to Stop It
Credential harvesting is the systematic collection of login credentials at scale, giving attackers authenticated access that bypasses perimeter defenses entirely. Stolen credentials remain one of the most common ways attackers gain initial access to organizations, and the volume of leaked credentials surged significantly in 2025. This guide covers the six methods attackers use, what happens inside a network after credentials are stolen, how credential harvesting creates compliance exposure under HIPAA, SOX, and GDPR, and how organizations close the gaps, including in frontline environments where shared devices compound the risk.
What is Identity Governance and Administration (IGA)?
Identity governance and administration (IGA) is the framework organizations use to define, review, and document who has access to what, across the full identity lifecycle. It sits above IAM, providing the policy layer that decides what access should exist, not just whether it works. Core IGA capabilities include access certifications, SoD enforcement, lifecycle management, and audit-ready compliance reporting for HIPAA, SOX, GDPR, and PCI DSS. This guide covers what IGA means, how it differs from IAM, what a working program includes, and where standard IGA assumptions break down in shared-device and frontline operational environments.
Salesforce Phishing-Resistant MFA 2026: Entra ID, AMR Signals, and How to Stay Compliant
Salesforce now enforces phishing-resistant MFA for privileged users across direct and SSO logins, and organizations on Microsoft Entra ID are running into a specific failure: users who completed MFA at Entra are being challenged again inside Salesforce because the token did not carry the right AMR signal. This blog covers what changed in 2026, how Salesforce evaluates AMR and ACR values, why the multipleauthn retirement blocked users mid-month, and how OLOID Face registered as an Entra External Authentication Method delivers the face AMR value Salesforce requires, with no hardware, no per-device enrollment, and no changes to your existing SSO configuration.
MFA vs Adaptive MFA
MFA vs adaptive MFA is one of the most consequential authentication decisions organizations face as credential-based attacks continue to accelerate. Traditional MFA applies a fixed second-factor challenge to every login regardless of context, while adaptive MFA evaluates real-time risk signals and adjusts the authentication requirement per attempt. This blog covers how both approaches work, where traditional MFA still holds up, where adaptive MFA has a clear operational advantage, and why the gap between them is most visible in shared-device and frontline environments. It also covers the passwordless-plus-adaptive combination and what to actually evaluate when selecting a solution.
IAM vs PAM: What's the Difference
IAM and PAM are two foundational access management disciplines that organizations frequently conflate, but they govern different users, different risks, and different layers of the security stack. IAM manages identity and access for the entire workforce. PAM focuses specifically on privileged accounts with elevated access to critical systems and data. Most organizations underestimate the gap between their IAM coverage and what PAM is actually designed to protect. That gap widens significantly in shared-device and shift-based environments such as healthcare, manufacturing, logistics, and retail, where standard access management assumptions break down. This guide covers what IAM and PAM are, how they differ, where each falls short on its own, and what organizations in high-stakes environments need to get both right.
Microsoft Passkey Migration: Timeline, Deadlines, and Admin Steps for Shared-Device Environments
Microsoft is retiring SMS and voice MFA in Entra ID across two dates: September 1, 2026 (passkeys auto-enabled) and February 1, 2027 (hard cutoff, no opt-out). Users still on SMS or voice after February 1 hit a blocking sign-in prompt they cannot skip. Standard passkey rollouts do not cover frontline workers or shared-device environments, which require a separate credential strategy. This post covers the full timeline, the admin audit steps, and the deployment gap most migration guides leave unaddressed.
What is Network Segmentation? A Complete Guide
Network segmentation is the practice of dividing a computer network into isolated subnets, each governed by its own security policies, to limit lateral movement and contain breaches. Most organizations treat it as a deployment checkbox rather than an ongoing discipline, which is where implementations degrade. This guide covers how segmentation works technically, why the perimeter trust model failed, how segmentation connects to Zero Trust and identity enforcement, where deployments typically go wrong, and how to implement a segmentation architecture that holds under real attack conditions, including in shared-device and frontline operational environments.
Authentication vs. Authorization: Key Differences Explained
Authentication and authorization are two distinct access control decisions that most organizations treat as one. Authentication verifies identity. Authorization enforces what that identity can reach. Conflating them is the most common reason broken access control remains the top web application security risk year after year. This guide covers how each layer works, the protocols behind them, where implementation breaks down in practice, and why shared-device and frontline environments need both layers designed differently from the ground up.

Making every day-in-the-life of frontline workers frictionless & secure!
Get the latest updates! Subscribe now!
