


About
Mona Sata is a B2B content and narrative specialist with experience in cloud-native and security technology. She translates complex concepts into clear messaging that helps technical teams communicate with authority and earn buyer trust.
Usually writes about

What is Virtual Desktop Infrastructure (VDI)? The Complete Guide
Virtual desktop infrastructure is the technology that hosts desktop environments on centralized servers and delivers them to users over a network, from any device. Most organizations understand VDI as a remote work tool, but its strongest use case is in shared-device environments where multiple workers rotate through the same terminals across shifts. This guide covers how VDI works, the difference between persistent and non-persistent deployments, where VDI fits inside a zero-trust security architecture, and where traditional VDI assumptions break down for frontline operations in healthcare, manufacturing, logistics, and retail.

What is the Client to Authenticator Protocol (CTAP) and Why Does It Matter
The client-to-authenticator protocol (CTAP) is the FIDO Alliance specification that governs how a browser or operating system communicates with an external authenticator, such as a security key, badge, or phone, over USB, NFC, or Bluetooth. Most organizations adopting passwordless authentication understand WebAuthn and FIDO2 at a surface level but miss how CTAP lies beneath both and enables hardware-bound authentication. The gap widens in operational environments: shared workstations, shift-based terminals, and frontline devices where standard authentication assumptions, one worker, one device, do not hold.
What is OAuth? A Complete Guide to Open Authorization
OAuth (Open Authorization) is an open standard protocol that lets applications access user data without ever handling a password. Most teams understand the surface-level concept but miss the implementation nuances that matter in practice: the right grant type, token lifecycle management, the deprecation of the implicit flow, and what changes with OAuth 2.1. This guide covers what OAuth is, how it works, which grant type fits each scenario, how it compares to OIDC, SAML, and SSO, and where token-based authorization becomes especially critical in shared-device and frontline environments.
What is Proximity Authentication?
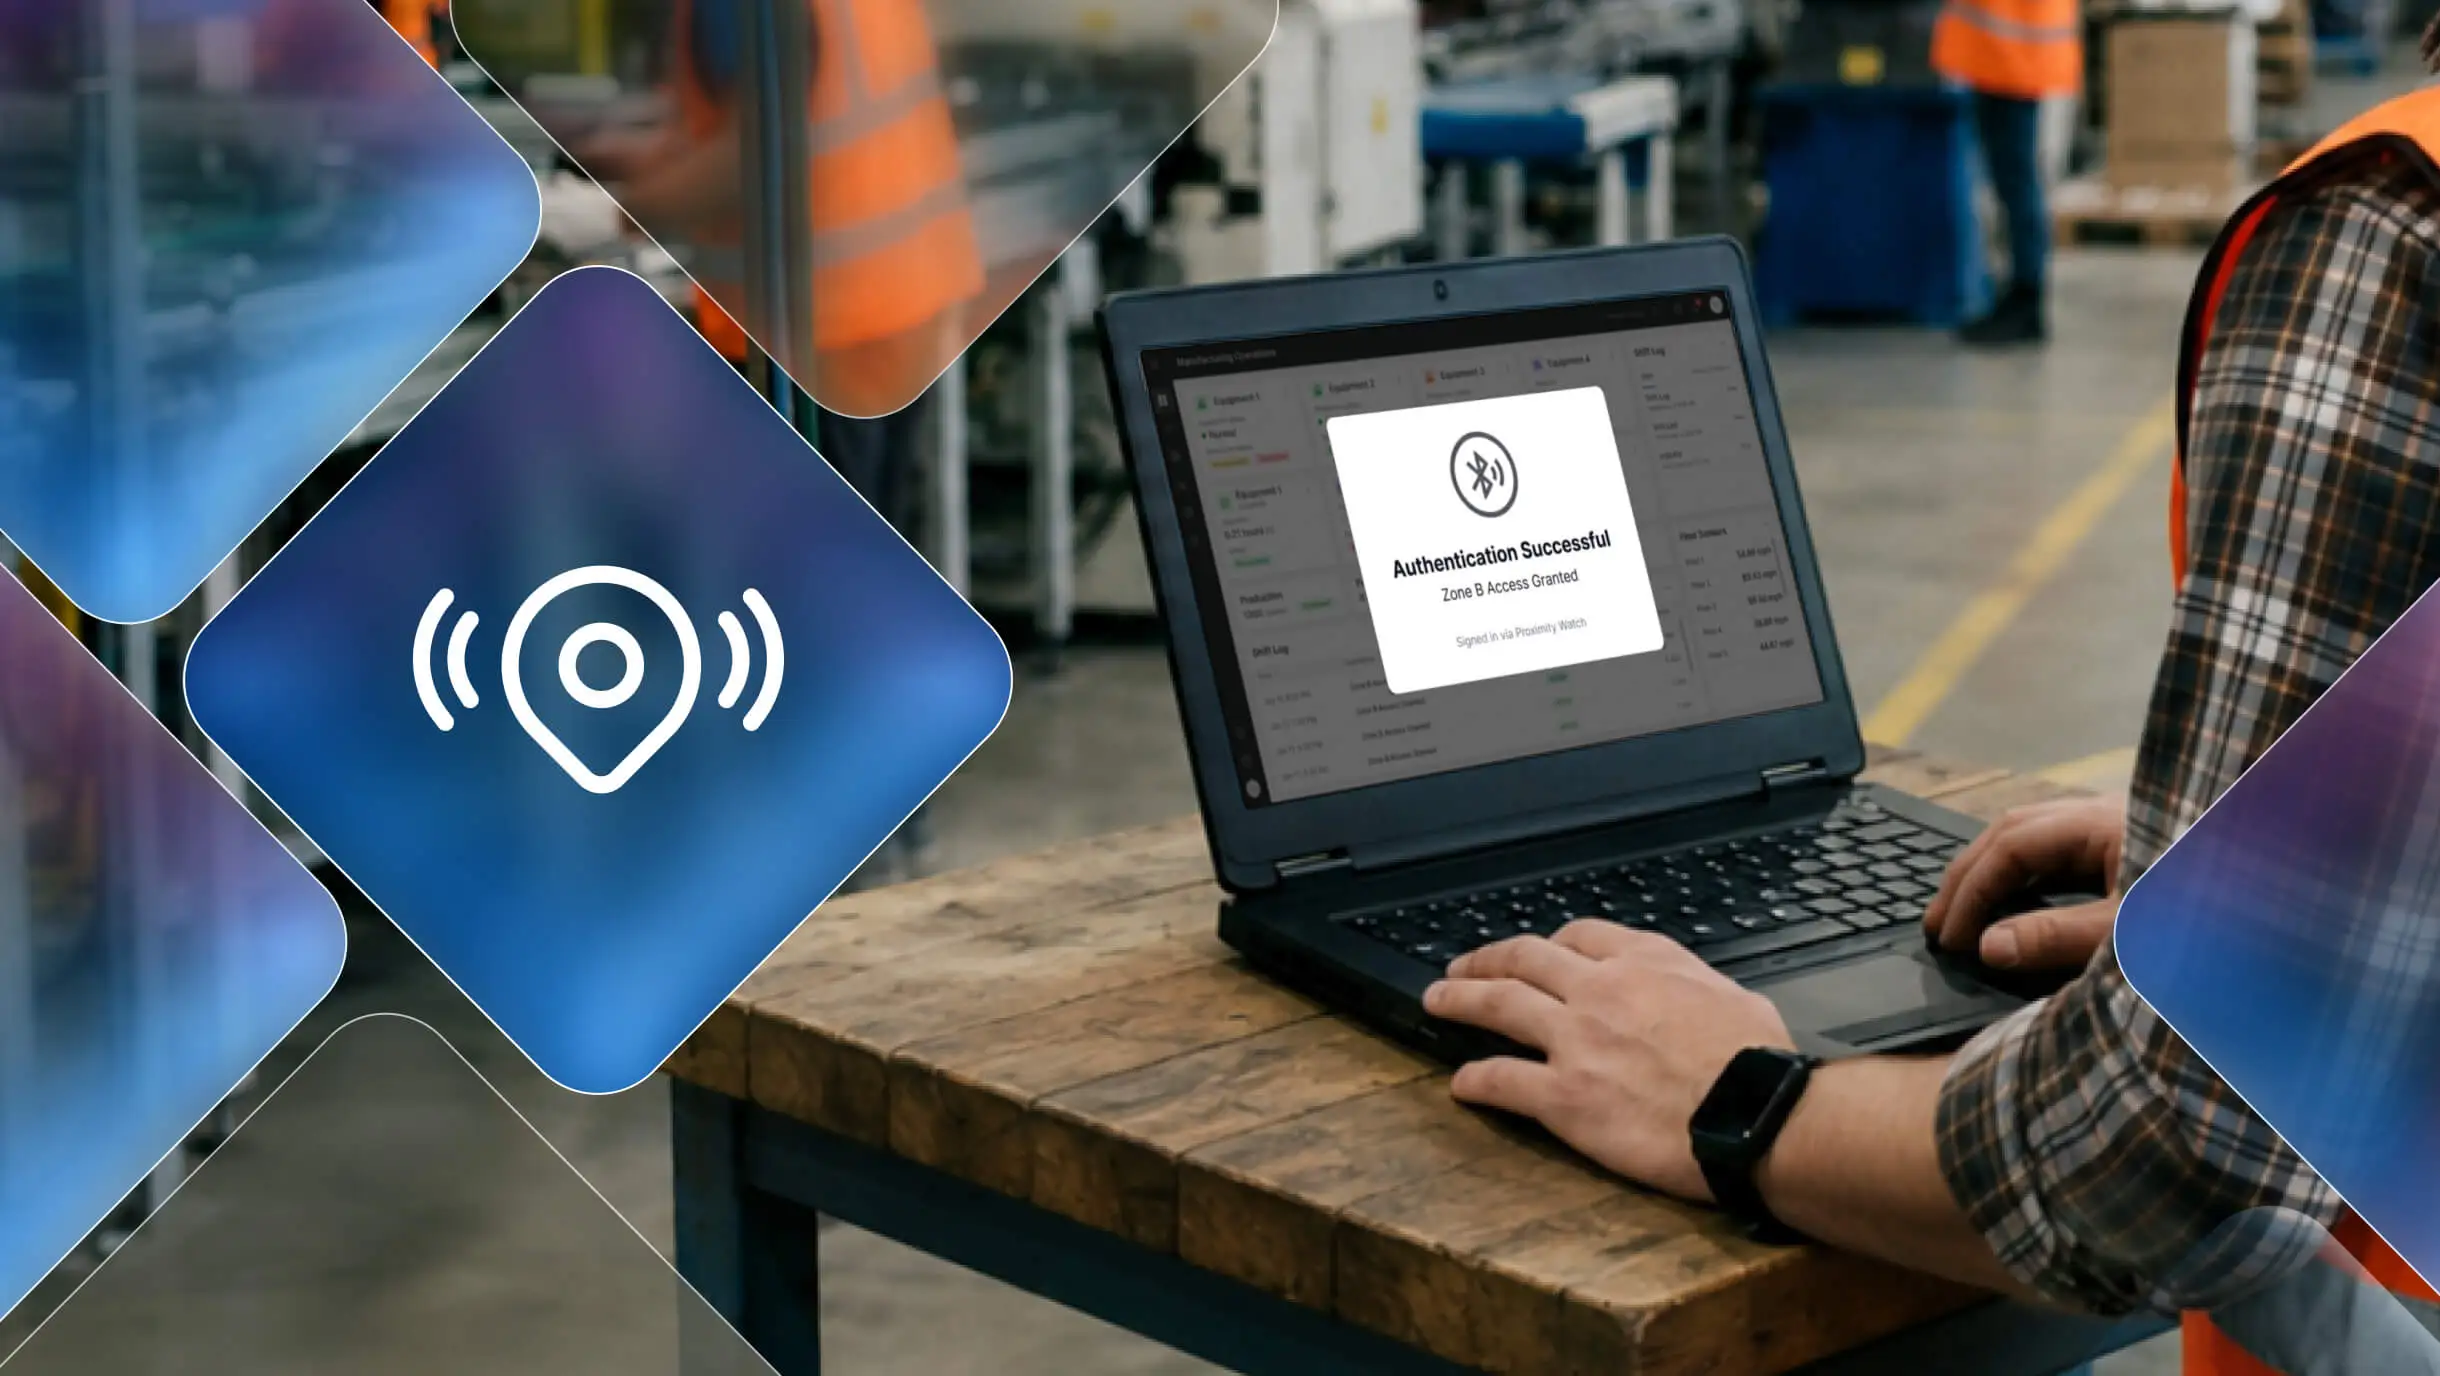
Proximity authentication verifies identity through physical presence, not passwords or PINs, using technologies like BLE, NFC, and Wi-Fi to detect how close a paired device is to a host system. When the user approaches, the session opens automatically. When they walk away, it locks. This blog covers how proximity authentication works, which communication protocols power it, how it compares to badge tap and biometrics, and where it delivers the strongest security and operational value. It also maps proximity authentication to HIPAA, CMMC, and PCI DSS compliance requirements and outlines what to consider before deployment, including token loss, signal interference, and fallback planning.
CMMC ITAR Access Control Checklist 2026: A Practical Guide
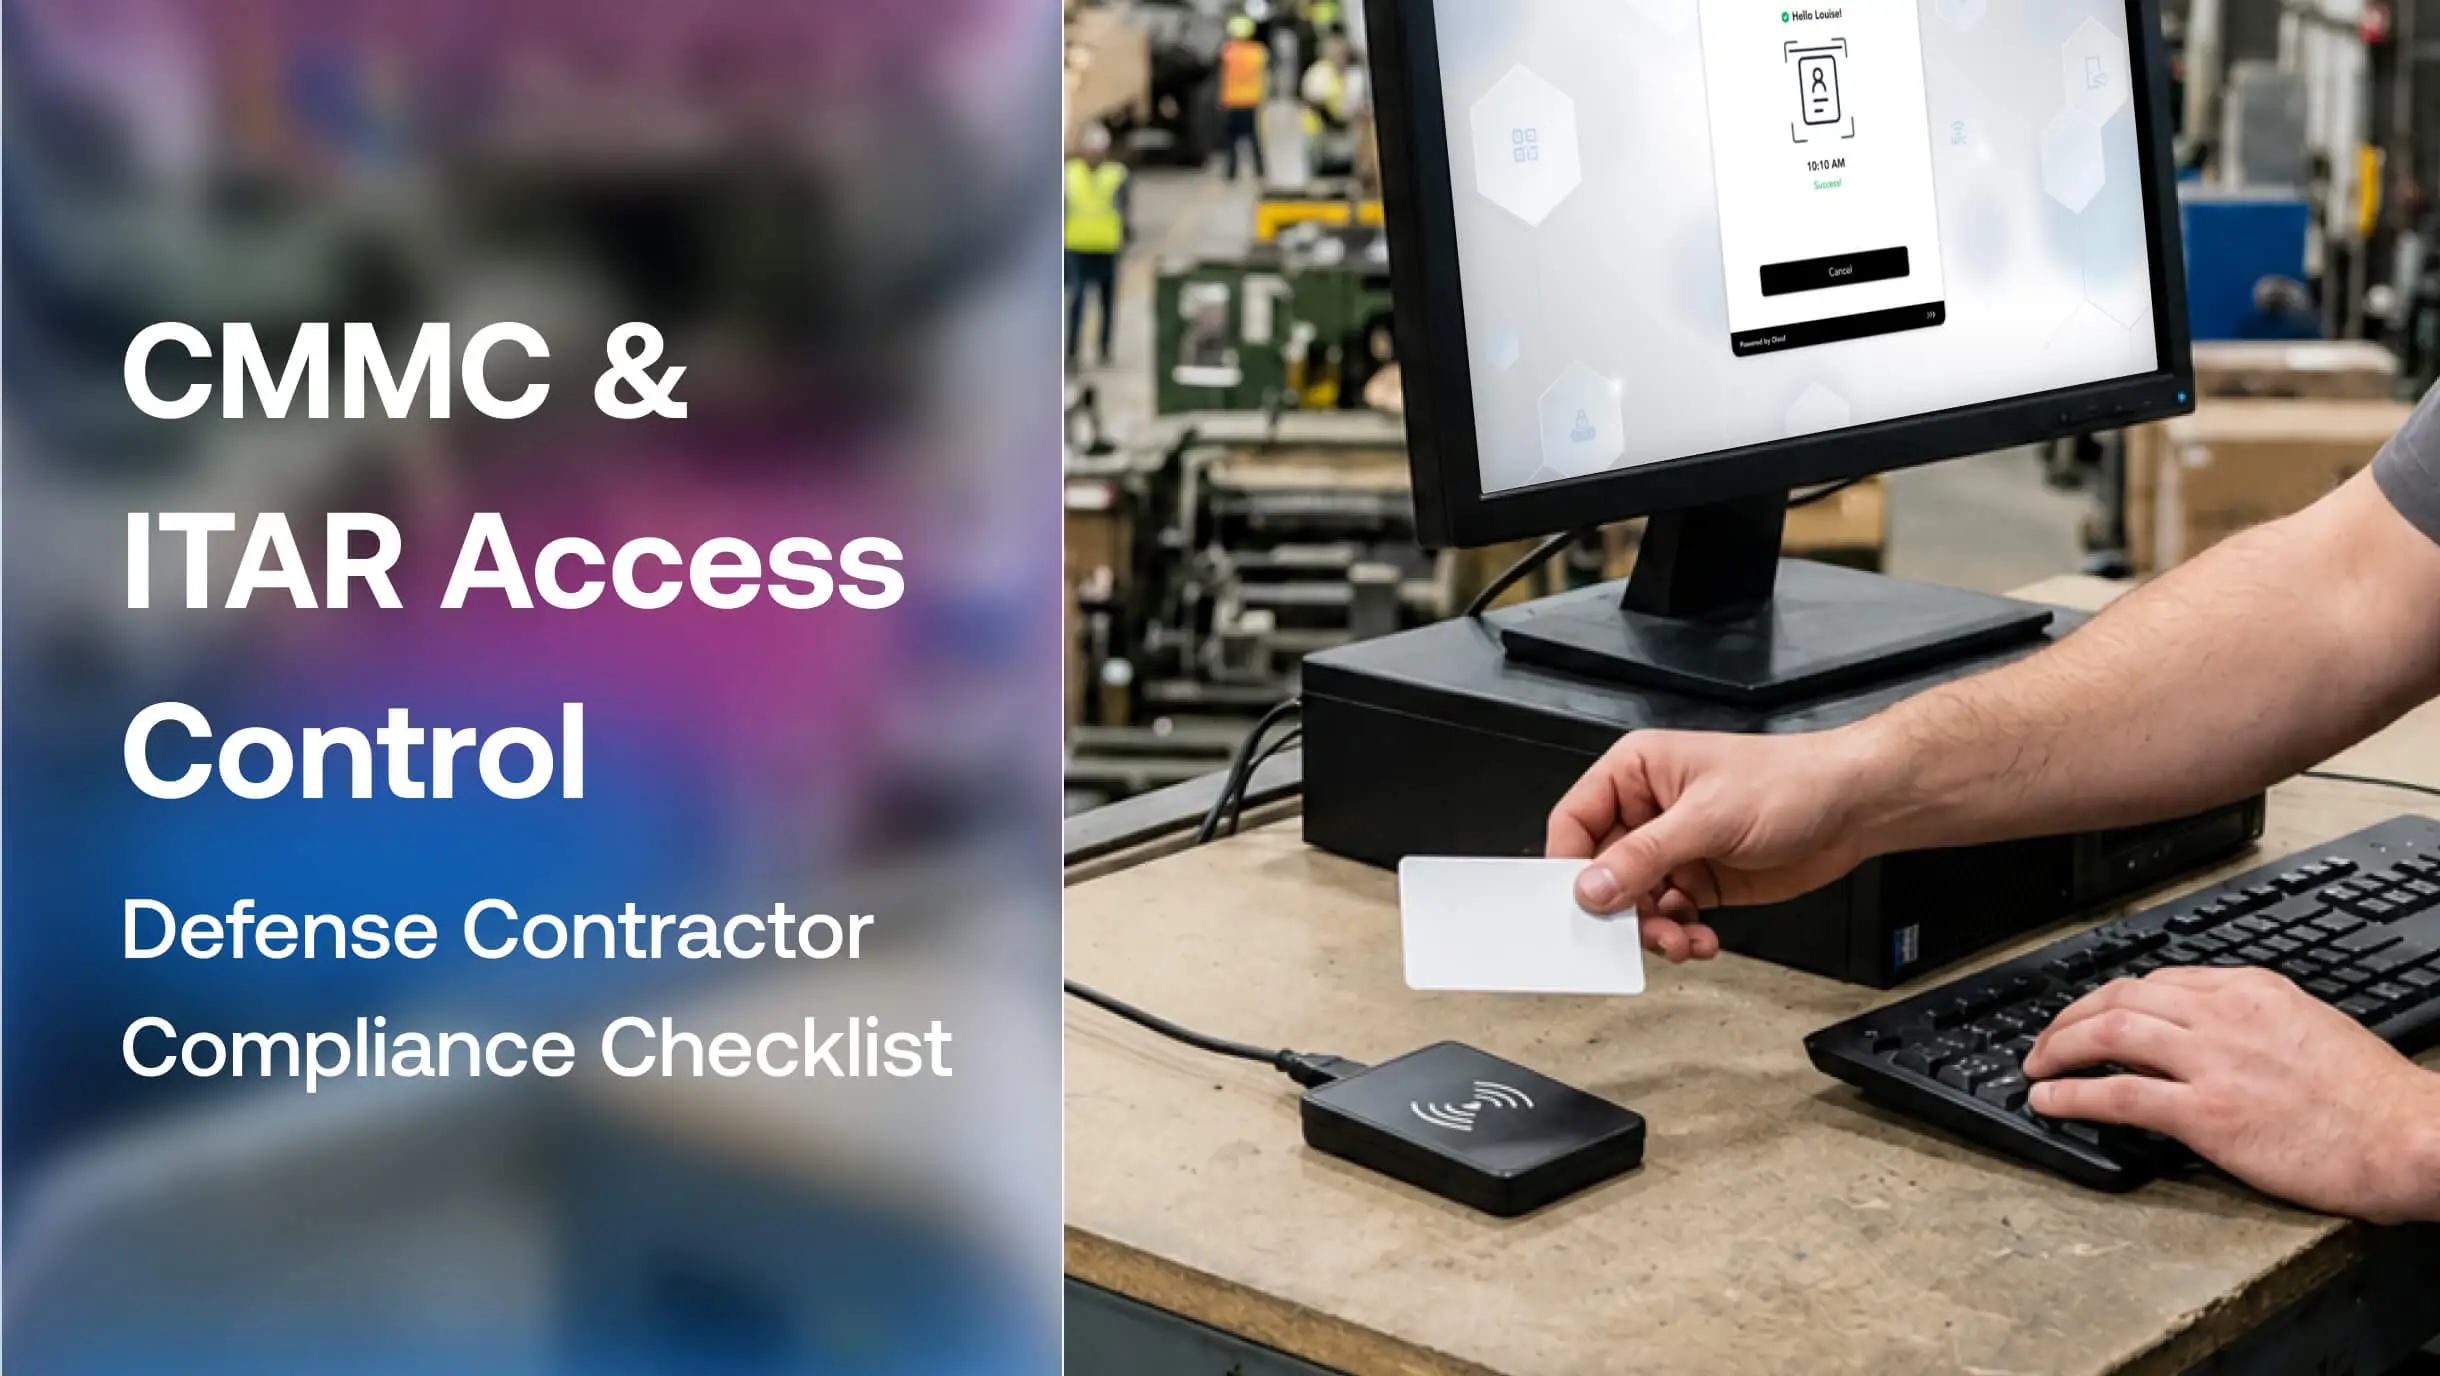
The CMMC ITAR access control checklist maps the 22 AC domain requirements from CMMC 2.0 and ITAR's identity-based access obligations into a single actionable framework for defense contractors. Most organizations in the Defense Industrial Base underestimate where their access controls break down in practice, particularly on shared production floor terminals, in mixed-nationality workforces, and during high-turnover offboarding cycles. This guide covers what CMMC and ITAR each require for access control, where the two frameworks overlap and where they diverge, what the November 2026 Phase 2 enforcement deadline means for AC domain readiness, and what compliant identity and access management looks like in defense manufacturing and operational environments.
PCI DSS Access Control Checklist 2026: A Practical Guide
The PCI DSS access control checklist governs who can access cardholder data environments, how they authenticate, and how every session gets logged and attributed to an individual. Most organizations underestimate where their access control program breaks down in practice, particularly around shared POS terminals, standing access after termination, and audit trails that collapse when credentials are shared. This guide covers all 12 PCI DSS requirements, explains what PCI DSS 4.0.1 changed for access control, and shows exactly where operational environments in retail, logistics, and manufacturing create persistent compliance gaps that standard checklists never address.

Making every day-in-the-life of frontline workers frictionless & secure!
Get the latest updates! Subscribe now!
