


About
Mona Sata is a B2B content and narrative specialist with experience in cloud-native and security technology. She translates complex concepts into clear messaging that helps technical teams communicate with authority and earn buyer trust.
Usually writes about
What is Fast User Switching: How It Works and Where It Breaks
Fast user switching lets a new user take over a shared device in seconds without a full logout, so every action stays tied to a verified individual. Most organizations treat it as a convenience feature and miss how much the implementation model matters. In a healthcare environment, where identity lives, how the previous session is handled and which authentication method healthcare professionals use decide whether switching protects the audit trail and the patient record or quietly breaks them. This guide covers the four switching models, their real-world failure points in clinical workflows, what an auditable switch records, and how to evaluate solutions for shared clinical workstations.
Passwordless Clinical Workflows: A Practical Guide
Passwordless authentication in healthcare replaces typed passwords with badges, biometrics, and passkeys that tie every clinical session to a verified individual. Shared workstations break the one-person-per-device model most identity tools assume, which drives open sessions, credential sharing, and broken audit trails. This guide compares passwordless methods for clinical settings and explains risk-based step-up for EPCS. It also covers identity across the clinician lifecycle, HIPAA and DEA alignment, and a phased rollout with measurable KPIs.
NIST Zero Trust Architecture: A Practical Guide
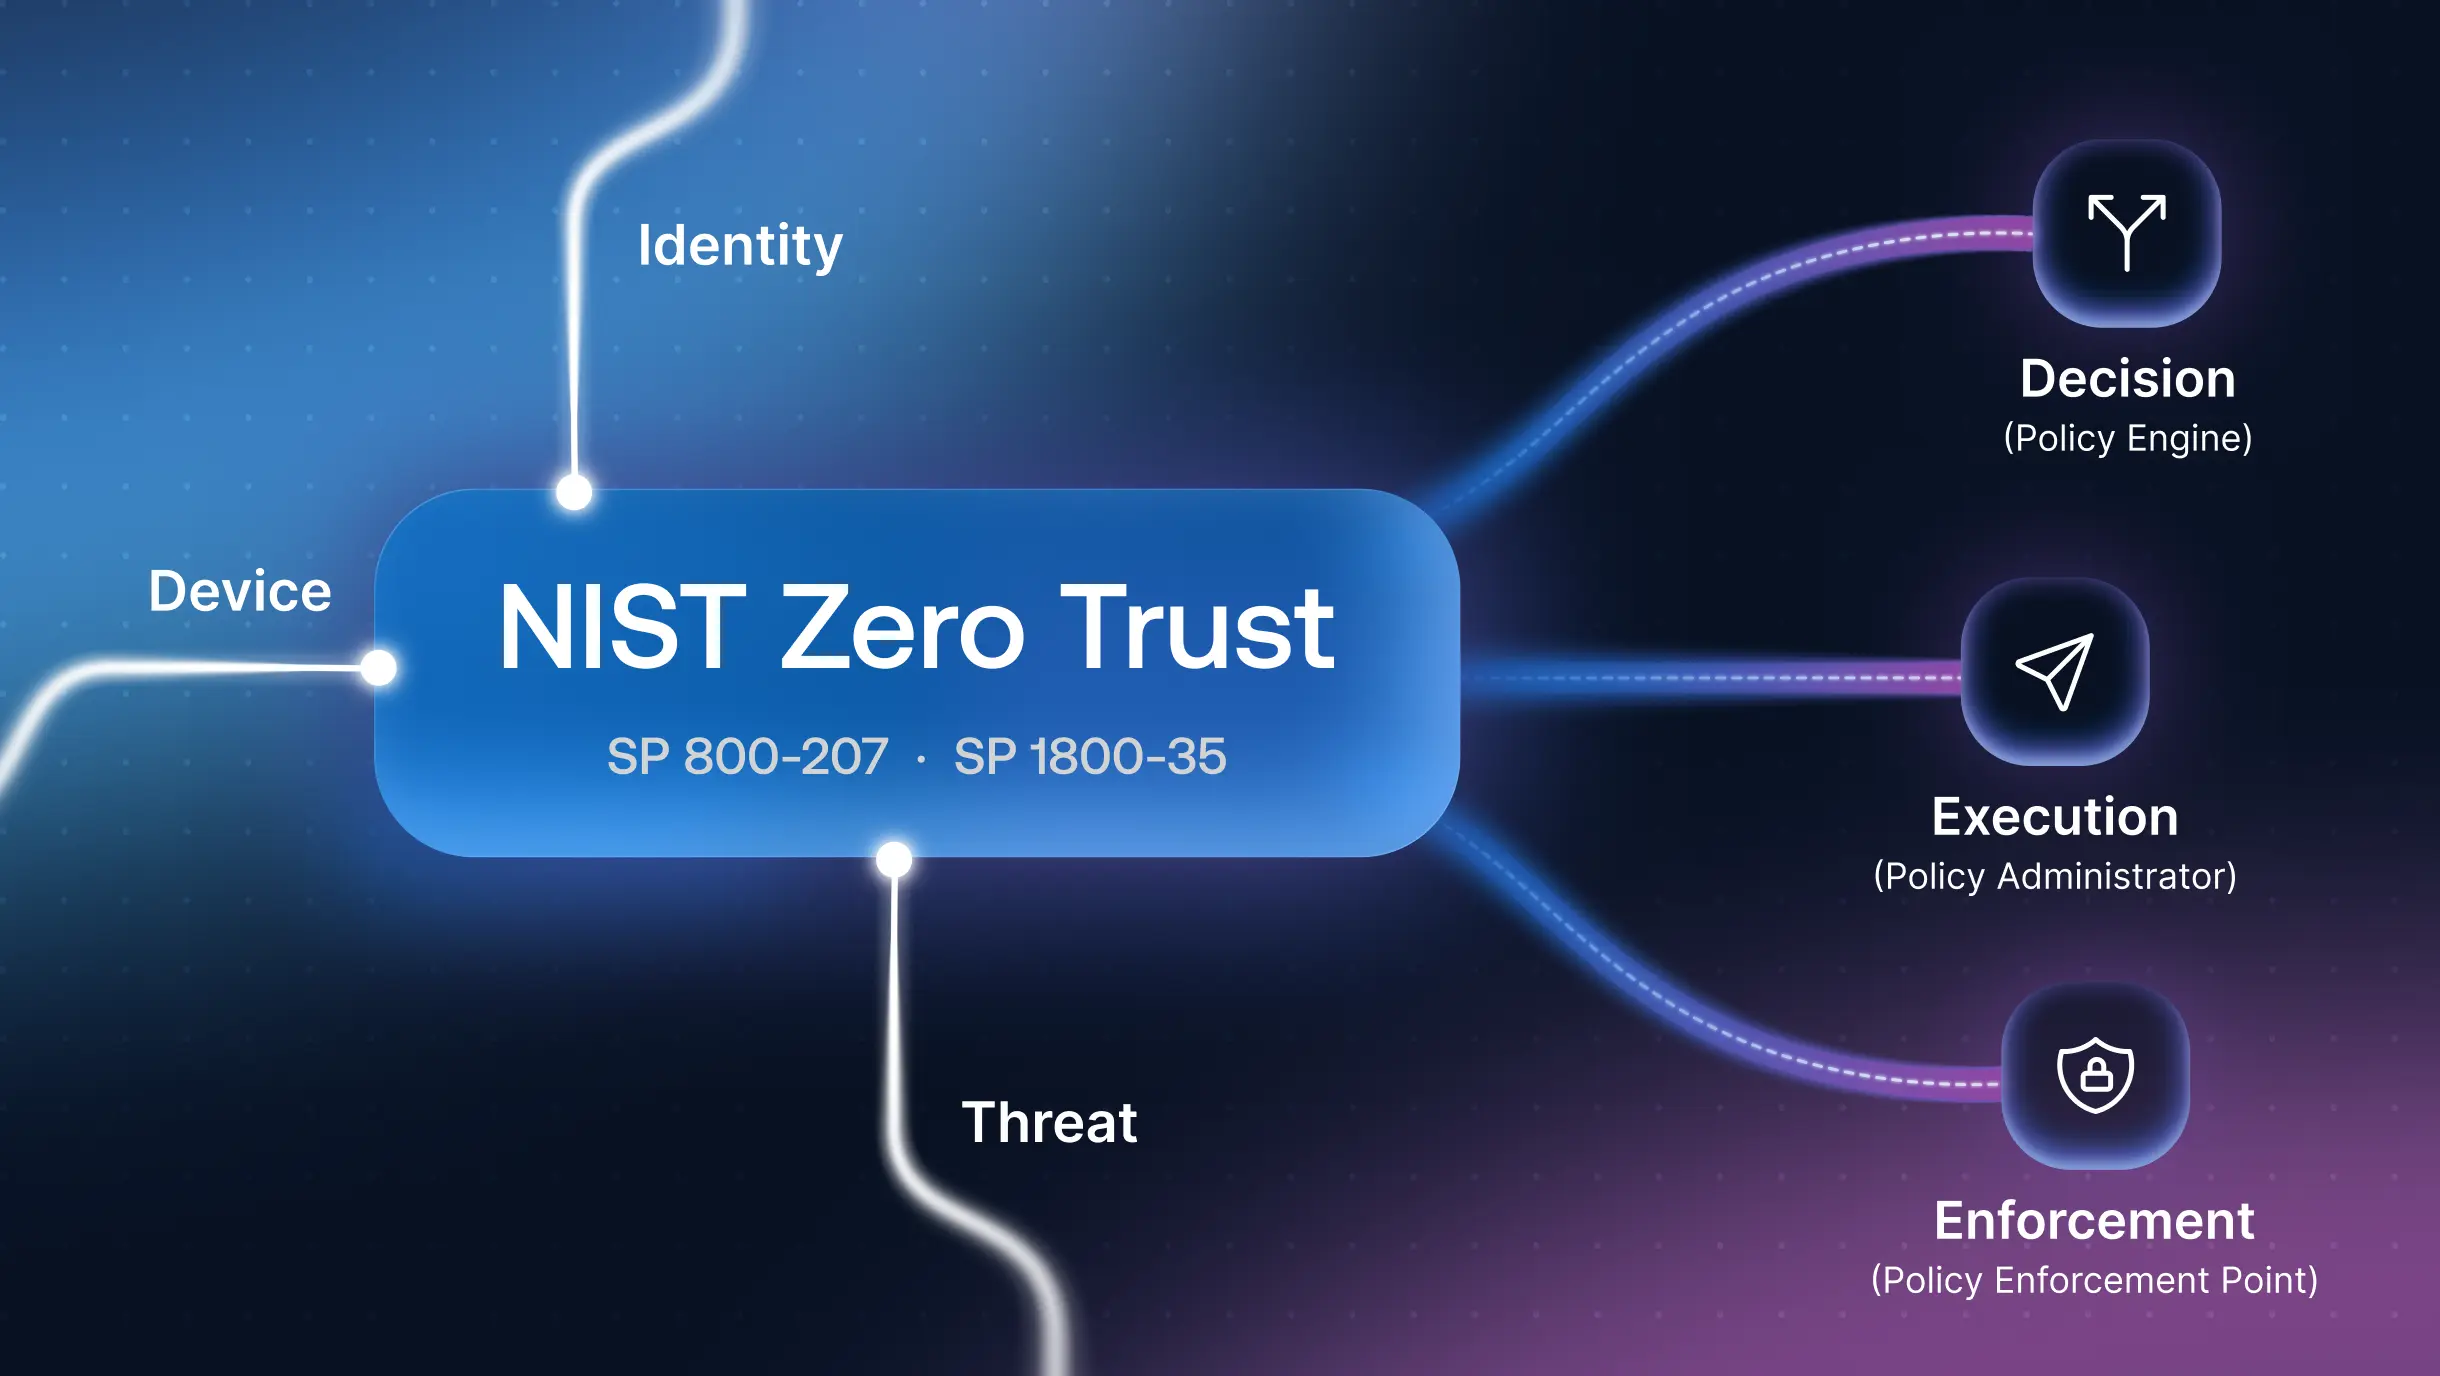
NIST zero trust architecture is a vendor-neutral security model that evaluates every access request using identity, device posture, and context instead of network location. SP 800-207 defines the model, and SP 1800-35 tests it through 19 implementations built with 24 vendors. This guide explains the reference components, how trust decisions are made, and what NIST's own builds revealed about integration gaps. It also covers the blind spot most programs miss: shared devices and frontline workers, where healthy endpoints can hide unverified users.
Passkey Enterprise Challenges: Why Frontline Environments Break the Model
Passkey enterprise challenges go deeper than legacy system integration and cross-platform fragmentation. The deployment gap most organizations do not plan for is workforce segmentation: standard passkey architecture, both device-bound and synced, was built for knowledge workers on managed devices, not for frontline workers rotating through shared terminals across shifts. This post covers where passkey deployment breaks structurally in shared-device environments, why compliance mandates accelerate pressure without solving the frontline problem, and what an authentication architecture that accounts for the full workforce actually looks like.
Multi-Factor Authentication Examples: Methods, Use Cases, and Best Practices
This guide covers the most common multi-factor authentication examples across the three-factor categories, comparing SMS OTPs, TOTP, push notifications, biometrics, and hardware security keys on security strength and operational fit. It maps MFA method selection to industry context including healthcare, manufacturing, financial services, and retail, and addresses where standard MFA breaks down on shared terminals when sessions are not tied to individual workers. The post closes with how passwordless authentication closes the individual attribution gap that conventional MFA leaves open in shift-based environments.
What is Privileged Identity Management (PIM)?
Privileged identity management (PIM) governs the lifecycle of elevated access roles: who holds them, under what approval, and for how long. This guide covers how PIM differs from PAM and IAM, how the role lifecycle works from request through automatic revocation, and why PIM breaks down in shared-device and frontline environments where multiple workers share terminals. It covers compliance requirements under HIPAA, PCI DSS, SOC 2, and NIST 800-53, and explains what individual-level attribution actually requires at the point of access. Practical best practices and a phased starting point are included.

Making every day-in-the-life of frontline workers frictionless & secure!
Get the latest updates! Subscribe now!
