


10 Key Passwordless Authentication Best Practices to Streamline Access Management
Passwordless authentication eliminates security vulnerabilities while improving user experience across organizations. This guide explores 10 essential passwordless authentication best practices. Following these proven strategies enables organizations to deploy secure, user-friendly authentication systems that reduce costs and enhance their security posture.

Passwords have long been the weakest link in digital security. From reused credentials to phishing attacks, traditional passwords expose organizations to constant risks while frustrating users with complex requirements.
That’s why businesses are rapidly shifting to passwordless authentication, an approach that replaces passwords with stronger, simpler, and more user-friendly methods such as biometrics, magic links, and hardware tokens. This shift isn’t just a trend; it’s a fast-growing market.
According to Grand View Research, the global passwordless authentication market is projected to surge from USD 21,071.7 million in 2024 to USD 55,702.8 million by 2030, growing at a CAGR of 17.1% between 2025 and 2030. But making the transition requires more than just turning off passwords.
To truly enhance security and deliver a seamless login experience, organizations need to follow proven best practices for deploying a passwordless authentication solution. In this blog, we’ll explore these passwordless authentication best practices, highlight common pitfalls, and share practical steps to help you implement passwordless authentication successfully.
1. Choose Secure and Appropriate Methods
Your passwordless authentication method selection directly impacts both security effectiveness and user adoption rates. The right choice reduces security vulnerabilities while creating a positive user experience that encourages compliance. Mismatched methods can lead to workarounds that compromise your entire security strategy.
Key Actions to Take
- Evaluate biometrics, hardware tokens, and mobile authenticators against your risk profile.
- Test multiple methods with small user groups before deploying them organization-wide.
- Consider user comfort levels and existing technical infrastructure capabilities.
- Prioritize solutions offering reliable backup options when primary methods fail.
- Conduct comprehensive risk assessments to identify current vulnerability gaps and areas for improvement.
- Match authentication strength to data sensitivity and compliance requirements.
2. Prioritize Multi-Factor Authentication (MFA)
Adding security layers to passwordless authentication creates robust protection against sophisticated attacks. MFA prevents single points of failure while maintaining the convenience benefits that make passwordless attractive.
This approach strikes a balance between strong security and user experience requirements that drive successful adoption. Modern MFA implementations, as discussed in this blog on the benefits and challenges of MFA, can maintain user convenience while significantly improving security posture.
Key Actions to Take
- Combine device certificates with biometrics for enhanced security verification.
- Require location verification for accessing highly sensitive systems and data.
- Implement adaptive authentication that adjusts requirements based on risk context.
- Design MFA around user workflows rather than forcing rigid security processes.
- Utilize streamlined authentication for routine tasks while maintaining secure administrative access.
- Deploy intelligent systems that recognize standard patterns and flag anomalies.
3. Address Phishing and Brute-Force Risks
Passwordless systems face evolving attack vectors that require proactive defense strategies. FIDO2 protocols and certificate-based authentication provide technical protection against common attacks. User education complements these controls by creating human barriers against social engineering attempts.
Key Actions to Take
- Implement FIDO2 protocols to prevent credential replay across different domains and applications.
- Deploy certificate-based authentication to effectively block credential stuffing attempts.
- Monitor authentication patterns continuously to identify suspicious access behaviors.
- Train employees to recognize and report suspicious authentication requests promptly.
- Develop incident response procedures tailored to authentication-related security events.
- Establish threat intelligence feeds to stay current with emerging attack techniques and tactics.
4. Plan for User and Device Management
Effective lifecycle management ensures authentication systems remain secure and functional throughout their operational lifespan. Clear processes reduce administrative overhead while maintaining consistent security policies. Well-planned management procedures prevent security gaps that could compromise your entire authentication strategy.
Key Actions to Take
- Establish straightforward enrollment procedures for user onboarding and device registration.
- Create workflows for updating permissions as user roles change over time.
- Implement comprehensive deprovisioning procedures for departing employees and contractors to ensure a seamless transition.
- Maintain accurate inventories of all authentication endpoints across your organization.
- Plan replacement scenarios for failed hardware tokens and malfunctioning biometric sensors.
- Develop alternative authentication pathways for users with disabilities or technical constraints.
5. Secure Biometric Data and Devices
Biometric data requires specialized protection approaches that differ from traditional credential security. Local storage minimizes the impact of breaches while privacy policies build user trust. Proper biometric security prevents identity theft and ensures regulatory compliance across different jurisdictions.
Key Actions to Take
- Store biometric templates locally on devices rather than in centralized databases.
- Use hardware security modules to encrypt biometric data when possible.
- Implement device attestation to continuously verify the integrity of the authentication endpoint.
- Establish transparent privacy policies that clearly outline the collection and protection of biometric data.
- Create automated retention policies that delete templates when employees leave.
- Conduct regular privacy impact assessments to maintain compliance and user trust.
6. Centralize and Federate Authentication
Authentication centralization reduces complexity while improving security control across your technology ecosystem. Federation enables seamless access between applications and partner organizations. This architecture strikes a balance between centralized policy management and distributed processing, ensuring optimal performance and a seamless user experience.
Key Actions to Take
- Deploy single sign-on systems to eliminate friction between applications and enhance user experience.
- Utilize identity federation protocols for seamless access to partner organizations.
- Design federation strategies supporting both cloud and on-premises applications.
- Implement intelligent session management that strikes a balance between security and user convenience.
- Establish secure trust relationships with external identity providers using standard protocols.
- Test federated authentication regularly to ensure reliable access during critical operations.
7. Adopt Context-Aware and Risk-Based Authentication
Intelligent authentication systems adjust security requirements based on real-time risk assessment and contextual factors. This approach provides robust protection while minimizing friction for legitimate users. Dynamic risk calculation enables appropriate responses to unusual access patterns without impacting everyday workflows.
Key Actions to Take
- Analyze user location patterns, device health, and behavioral indicators to assess risk.
- Require additional verification for unusual access patterns and high-risk scenarios.
- Implement machine learning algorithms that improve risk assessment accuracy over time.
- Establish baseline user behaviors to identify meaningful security anomalies.
- Establish clear policies that define risk thresholds and outline appropriate authentication responses.
- Regularly tune systems to maintain effectiveness against evolving security threats.
8. Ensure Compliance with Industry Standards & Regulations
Regulatory compliance becomes manageable when authentication aligns with established industry standards. Proper documentation and audit capabilities satisfy regulatory requirements while reducing legal liability. Standards-based implementation simplifies vendor selection and system integration across different platforms.
Key Actions to Take
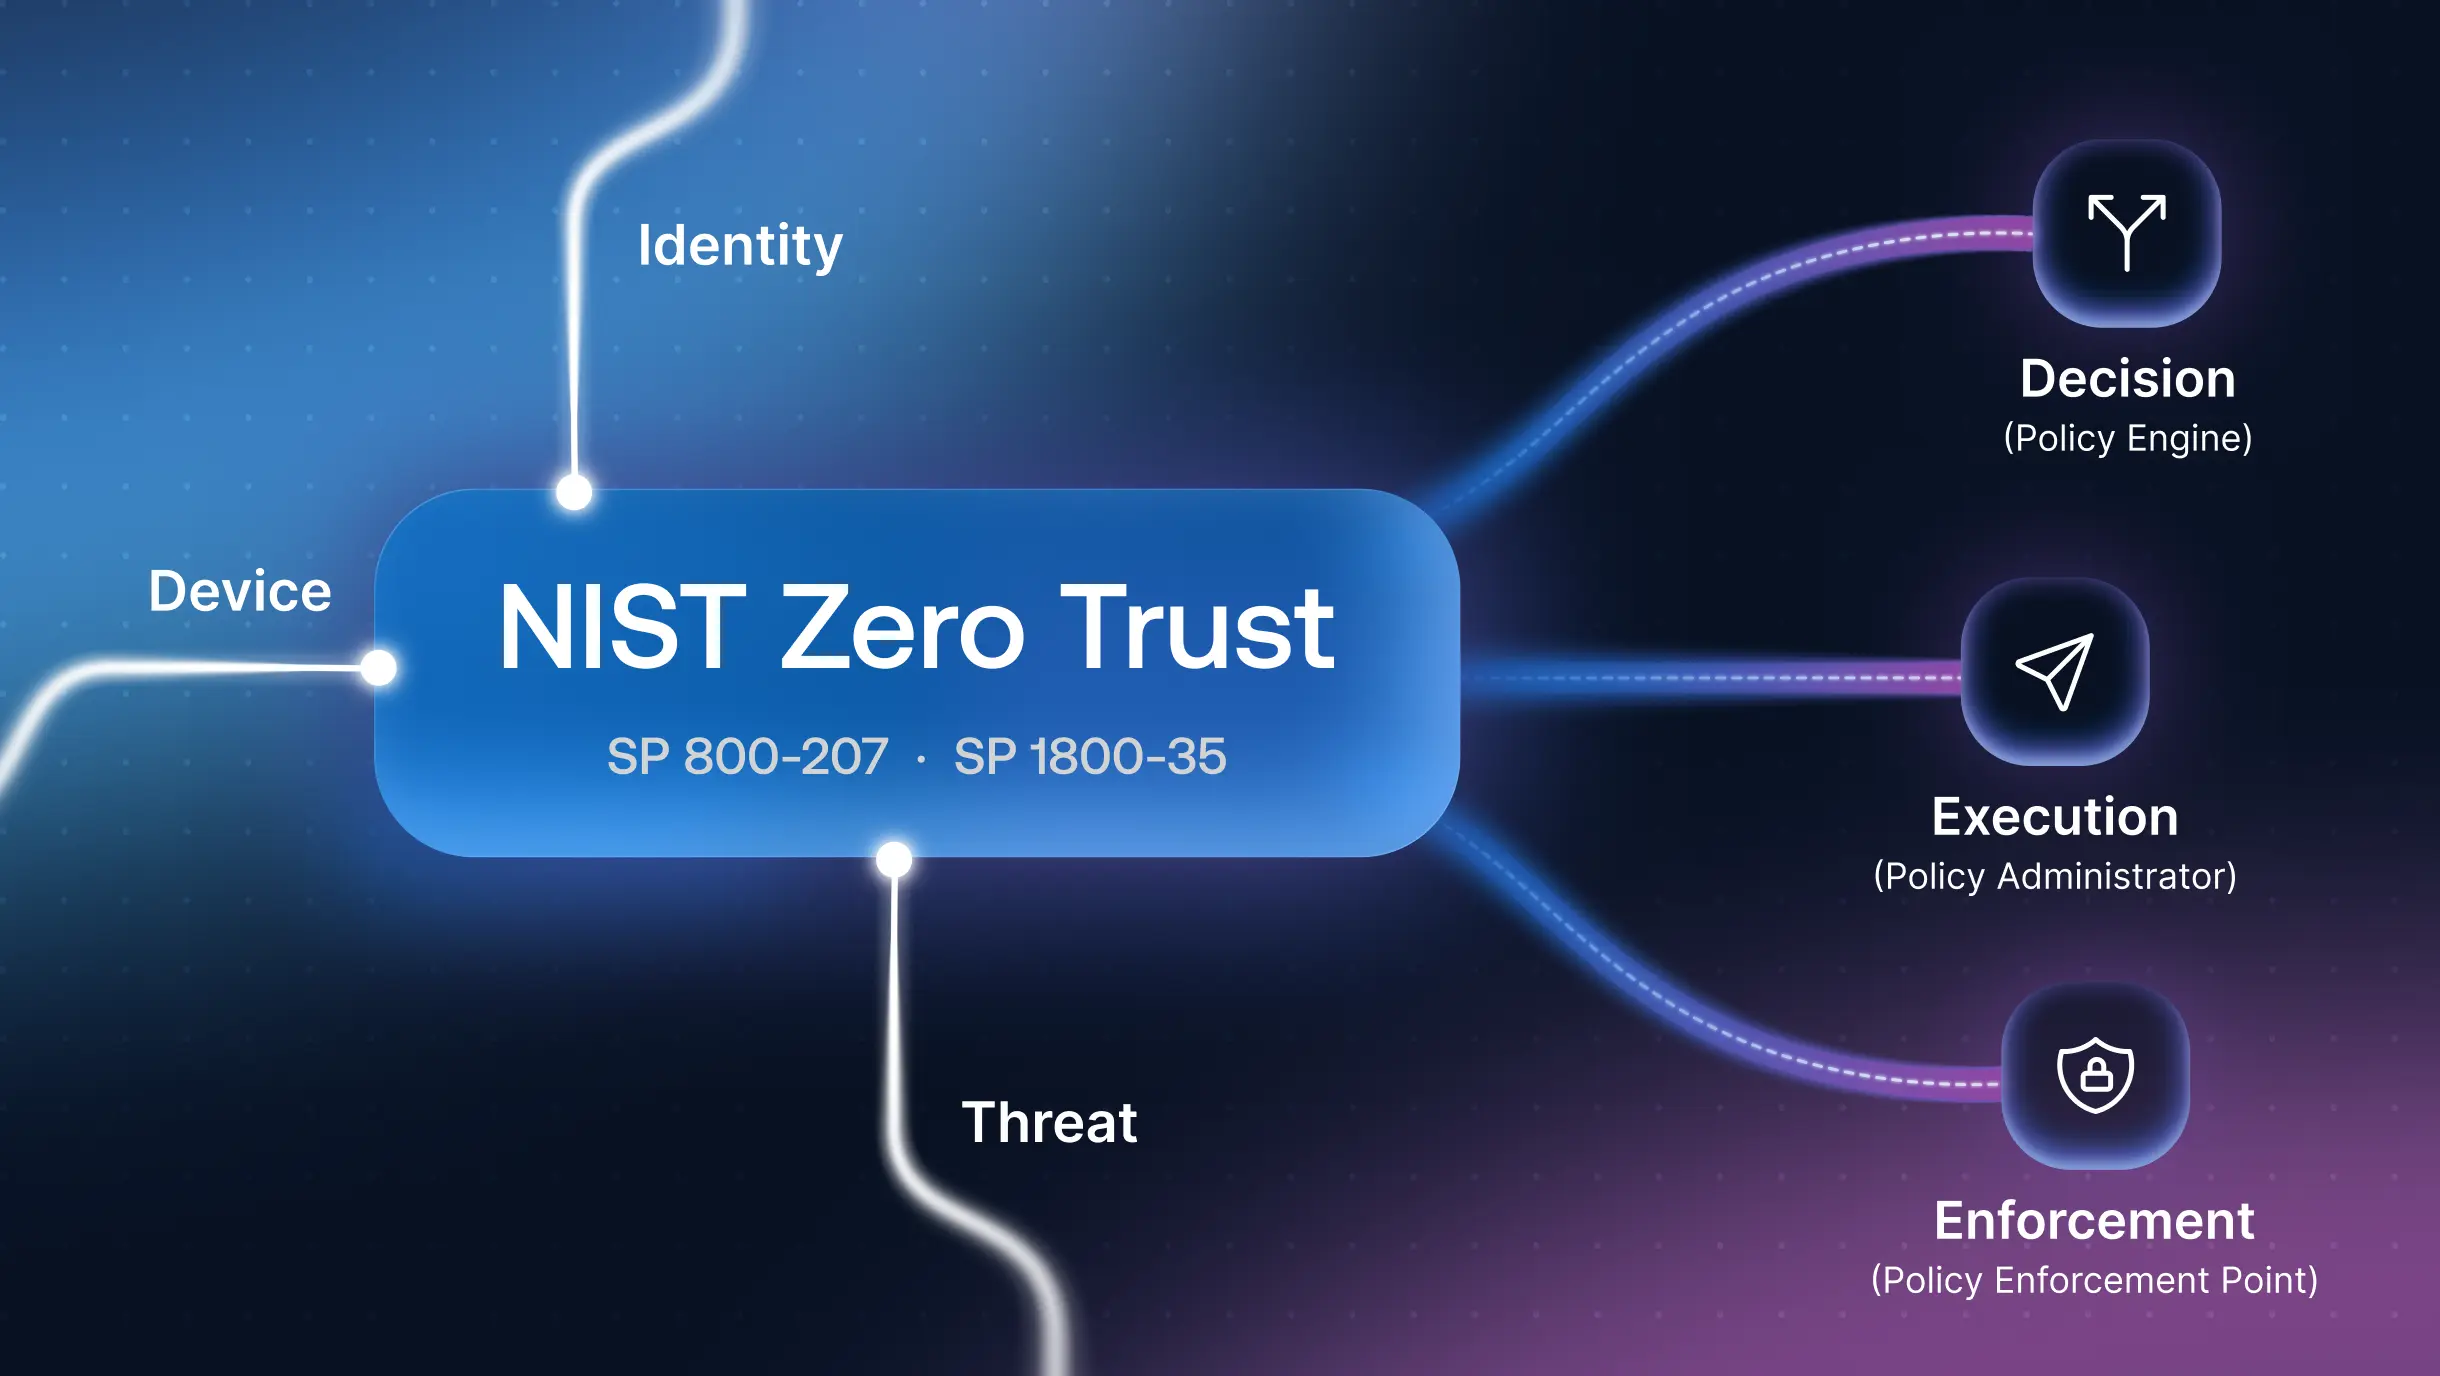
- Align implementation with FIDO2 standards for interoperability and security assurance.
- Thoroughly document authentication processes to meet regulatory requirements, such as GDPR and HIPAA.
- Implement comprehensive audit logging that captures compliance data without compromising privacy.
- Create real-time compliance dashboards providing visibility into system status.
- Collaborate with legal and compliance teams to understand specific regulatory requirements.
- Maintain current compliance training for technical teams on changing requirements.
9. Promote User Education and Support
User adoption success depends on comprehensive education and ongoing support throughout the implementation process. Well-informed users become active participants in security rather than obstacles to overcome. Effective support reduces frustration and prevents workarounds that could compromise security.
Key Actions to Take
- Train employees on proper authentication practices and general security awareness to enhance their overall security posture and protect sensitive information.
- Provide clear guidance for device enrollment and common troubleshooting scenarios.
- Create dedicated support channels specifically for authentication-related problems.
- Develop user-friendly documentation, video tutorials, and interactive guides to enhance the user experience.
- Establish help desk protocols that support passwordless authentication for password-related issues.
- Implement feedback mechanisms that allow users to report issues and suggest improvements.
10. Monitor, Audit, and Update Regularly
Continuous monitoring provides the foundation for effective security management in authentication. Regular assessments identify vulnerabilities while automated responses enable rapid incident resolution. Ongoing updates ensure systems remain effective against evolving threats and changing business requirements.
Key Actions to Take
- Implement comprehensive logging to track authentication events and identify security incidents.
- Schedule regular security assessments of the entire authentication infrastructure to ensure optimal security and compliance.
- Update policies and technologies promptly as new threats emerge.
- Establish key performance indicators measuring system health and security effectiveness.
- Deploy automated alerting for failures, suspicious patterns, and performance issues.
- Develop incident response playbooks specifically for authentication-related security events.
These are the 10 best practices for passwordless authentication, reshaping how businesses are managing access control. Implementing these best practices, along with a reliable passwordless authentication tool, can streamline identity and access management.
How OLOID is Transforming Passwordless Authentication for Frontline Workers
Passwordless authentication isn’t just a security trend; it’s quickly becoming a necessity. By following the best practices we’ve covered, organizations can enhance protection against credential-based attacks while creating a faster and more intuitive login experience for their workforce.
This is where OLOID makes the difference. Designed specifically for the unique challenges of frontline environments, OLOID goes beyond generic passwordless tools. Our platform delivers secure, usernameless, and truly password-free authentication, reducing friction, eliminating password management hassles, and maximizing worker productivity.
With OLOID, enterprises can confidently adopt a future where security and usability work in harmony. The platform integrates seamlessly with current SSO systems, HRIS platforms, and MDM solutions without disrupting operations.
Automated credential provisioning reduces IT overhead while maintaining security across various industries, including manufacturing, healthcare, and retail. This approach eliminates password-related friction while strengthening security for frontline teams.
Ready to transform your frontline passwordless authentication experience? Book a demo to see how OLOID can streamline access for your workforce.

Get the latest updates! Subscribe now!

